Question #56
HOTSPOT –
You have an Azure Active Directory (Azure AD) tenant.
You plan to use Azure Monitor to monitor user sign-ins and generate alerts based on specific user sign-in events.
You need to recommend a solution to trigger the alerts based on the events.
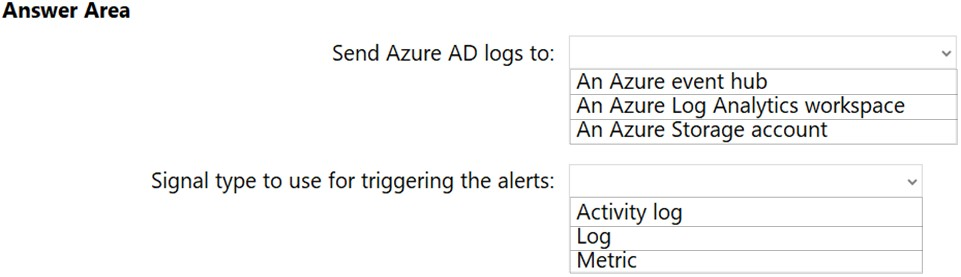
What should you include in the recommendation? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Hot Area:
Correct Answer:
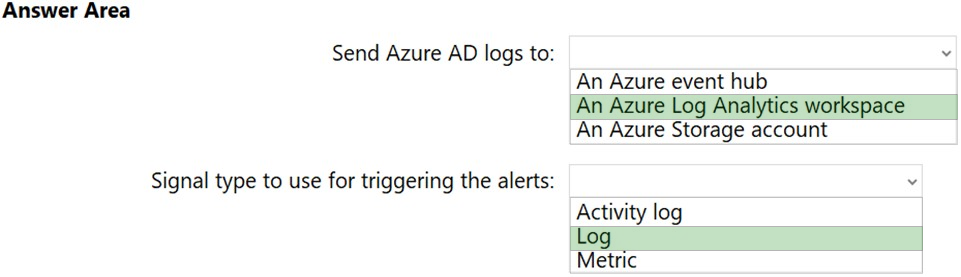
Box 1: An Azure Log Analytics workspace
To be able to create an alert we send the Azure AD logs to An Azure Log Analytics workspace.
Note: You can forward your AAD logs and events to either an Azure Storage Account, an Azure Event Hub, Log Analytics, or a combination of all of these.
Box 2: Log –
Ensure Resource Type is an analytics source like Log Analytics or Application Insights and signal type as Log.
Reference:
https://4sysops.com/archives/how-to-create-an-azure-ad-admin-login-alert/ https://docs.microsoft.com/en-us/azure/azure-monitor/platform/alerts-log