
⚠️ Retired / Legacy Exam: This exam has been retired or replaced. These practice questions are kept for reference only. Please check the official vendor website for current exam versions before studying.
An analyst is examining a system that is suspected of being involved in an intrusion. The analyst uses the command ‘cat/etc/passwd’ and receives the following partial output:
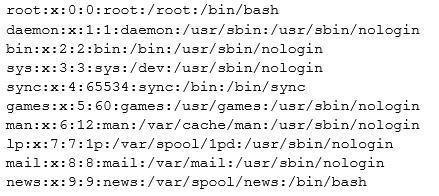
Based on the above output, which of the following should the analyst investigate further?
A. User ‘daemon’ should not have a home directory of /usr/sbin
B. User ‘root’ should not have a home directory of /root
C. User ‘news’ should not have a default shell of /bin/bash
D. User ‘mail’ should not have a default shell of /usr/sbin/nologin