
⚠️ Retired / Legacy Exam: This exam has been retired or replaced. These practice questions are kept for reference only. Please check the official vendor website for current exam versions before studying.
A technician receives the following security alert from the firewall’s automated system:
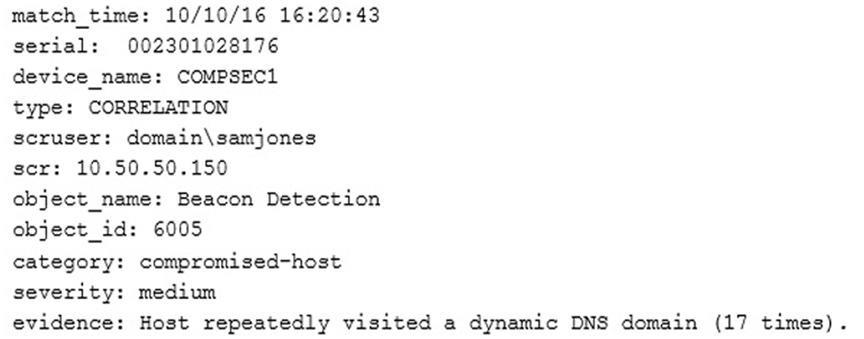
After reviewing the alert, which of the following is the BEST analysis?
A. This alert is a false positive because DNS is a normal network function.
B. This alert indicates a user was attempting to bypass security measures using dynamic DNS.
C. This alert was generated by the SIEM because the user attempted too many invalid login attempts.
D. This alert indicates an endpoint may be infected and is potentially contacting a suspect host.